Digital · Copenhagen
Denmark reports national registry breach exposing records of 8.8 million people
Unauthorised actors compromised personal records belonging to 8.8 million people in Denmark by abusing credentials assigned to a private company. Digitalisation Minister Christina Egelund announced the breach of the Central Person Register on 5 October 2026.
AI text based on reports by Le Monde.fr, Deutsche Welle, Courrier international and other publishers. Changed . How it is made
 Pollar Films · recorded Oct 6
For membersThe first 30 seconds for everyone. Synthetic voice (AI).
ExplainerSynthetic voice (AI)
Why was confidential data across Denmark exposed by a single breach?
In brief
The breach compromised records for 8.8 million individuals out of 11 million total entries stored in the Central Person Register.
Attackers gained entry by misusing search access granted to an authorized private Danish enterprise throughout September 2026.
Financial and banking credentials were not accessed, and individuals enrolled in address protection programmes were excluded.
Digitalisation Minister Christina Egelund blocked the compromised company's access and ordered a comprehensive security review on 5 October 2026.
- September 2026Unauthorised queries occur inside the Central Person Register.
- 2 OctAdministrators detect irregular system activity.
- 5 OctThe Ministry of Digital Affairs announces the security incident.
Breach of the population registry
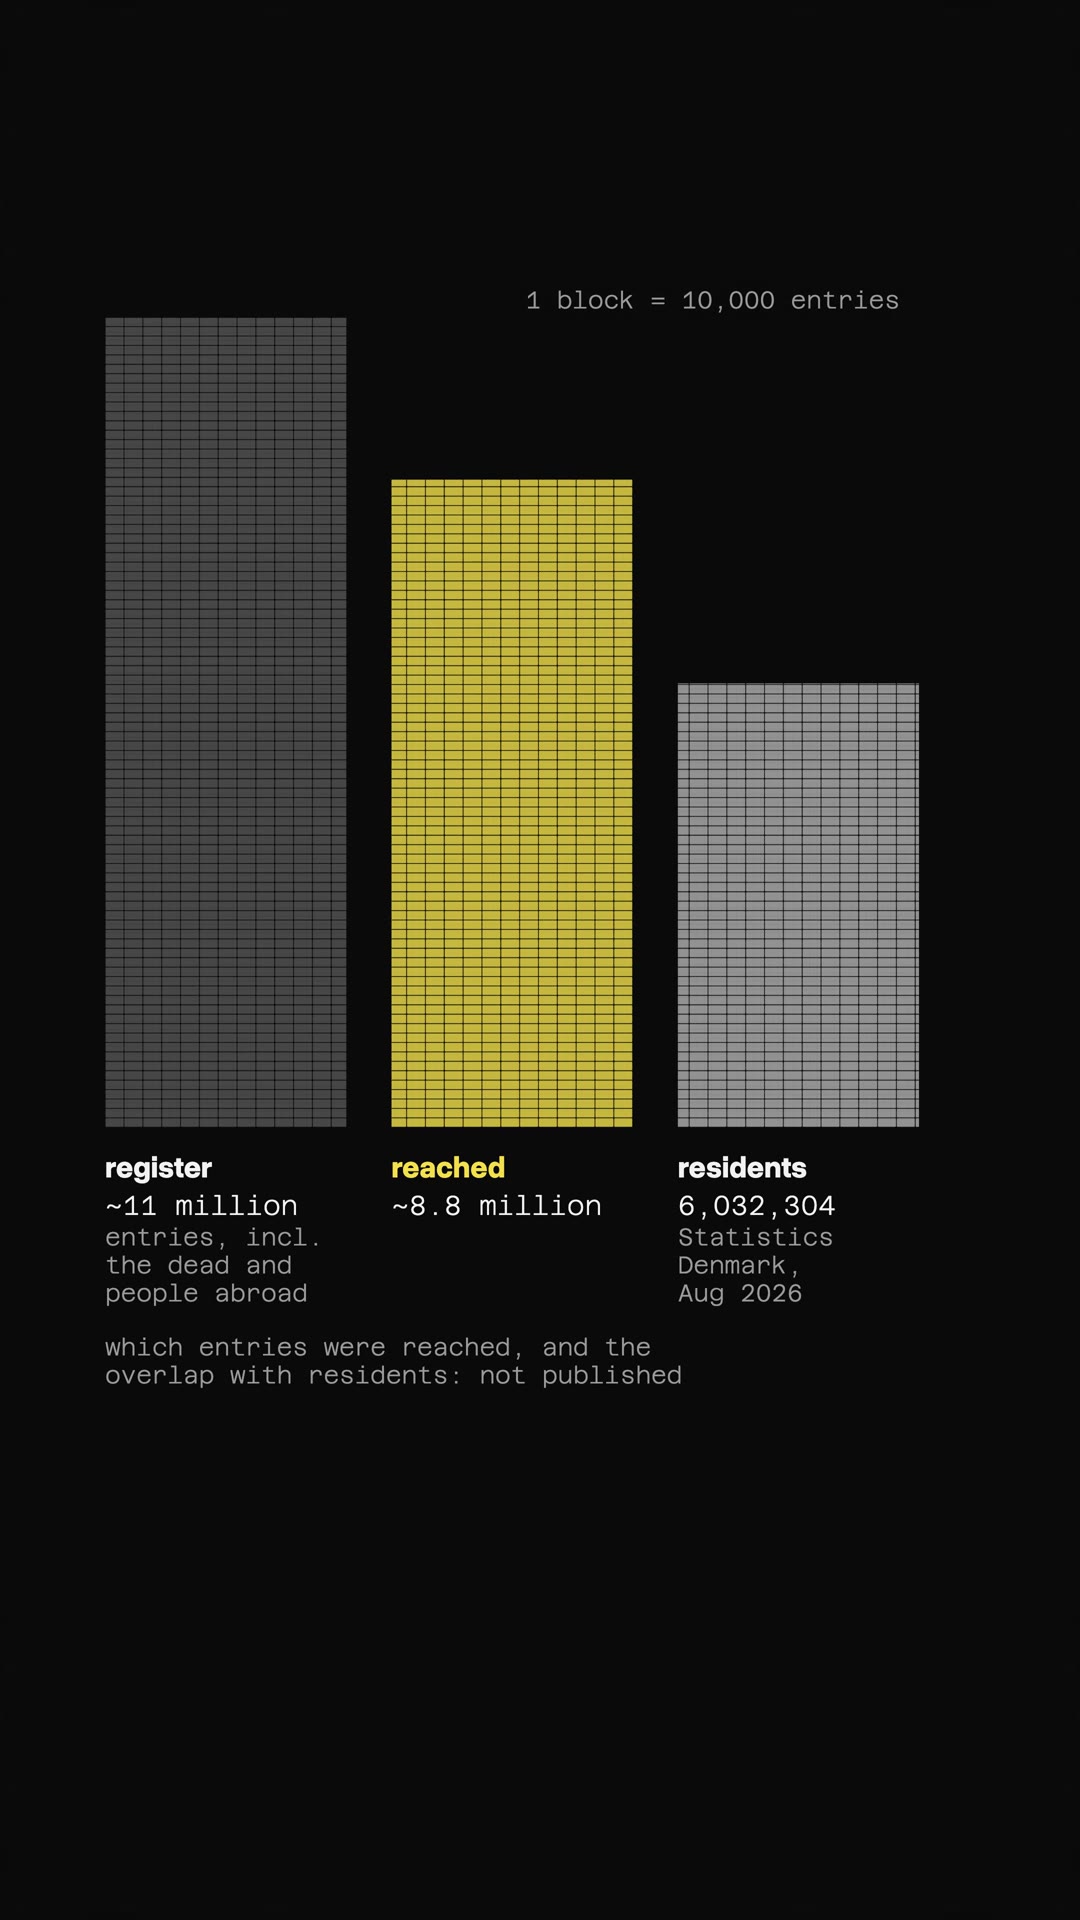
The Danish Ministry for Science, Higher Education and Digital Affairs announced on Monday morning, 5 October 2026, that unauthorized individuals breached the country's Central Person Register (CPR). The incident compromised the personal details of approximately 8.8 million registered persons, encompassing living citizens, residents, deceased individuals, and citizens who have relocated abroad. Information exposed in the breach includes full names, postal addresses, digital contact information, telephone numbers, and unique 10-digit personal identification numbers. While Denmark maintains a resident population of around 6 million people, the CPR system contains entries for roughly 11 million individuals spanning multiple decades. The compromised dataset accounts for the vast majority of all records preserved within the national database.
- Total CPR records
- 11 million
- Compromised records
- 8.8 million
- Living population
- 6 million
Data from the article text
Method and timeline of intrusion
Database administrators initially detected an anomaly in the registry system on 2 October 2026, launching an immediate assessment over the following weekend. Investigators determined that unauthorized database queries had been conducted throughout September 2026. The actors gained entry by exploiting the valid search permissions of an authorized private Danish enterprise, which maintained legitimate access to verify personal information with government records. Authorities responded by immediately severing the private company's access to prevent further queries across the registry. Danish police and cyber investigators opened a formal inquiry to trace the source of the intrusion, though the government stated that the perpetrators have not yet been identified.
Scope of registry data and exemptions
The unique 10-digit CPR number forms a fundamental pillar of Denmark's public and commercial administration, functioning as the primary identifier for tax assessments, health service records, and commercial banking operations. Beyond standard identity markers, the registry stores administrative details including church membership, legal incapacitation records, and restrictions on individual legal capacity. The Danish government confirmed that banking credentials and financial account numbers were not held within the exposed dataset and remained uncompromised. In addition, individuals who had previously enrolled in specialized state protection programmes for names and addresses were excluded from the exposed search results. Private entities in Denmark routinely utilize regulated system connections to verify citizen identities against the central registry during commercial transactions, making the protection of these access pathways critical to national data security.
Government response and public guidance
Digitalisation Minister Christina Egelund addressed the security failure on 5 October, ordering a comprehensive security audit of the registry infrastructure and its external access protocols.
“This is an extremely serious incident.”
Egelund noted that multiple state agencies and security services are collaborating to evaluate the technical scale of the data extraction.
“Together with all the relevant authorities, we are proceeding to reconstruct the full scope of the incident.”
The ministry warned residents across Denmark to prepare for potential identity fraud, deceptive telephone calls, and tailored phishing messages stemming from the compromised registry information. Egelund encouraged citizens to exercise heightened skepticism toward unsolicited outreach, avoid clicking unfamiliar internet links, and refrain from sharing sensitive credentials when contacted by unknown parties.
Ask about this text
Sources and context
- Christina Egelund
- Danish Minister for Digital Affairs
- Places
- Copenhagen, Denmark
Pollar is free and carries no ads in the text. Its members keep it going.
Support Pollar